Risk-based vulnerability management: How findings become the right priorities

In modern IT operations, prioritizing vulnerabilities based solely on CVSS scores is no longer sufficient. Risk-based vulnerability management combines technical severity with threat intelligence, endpoint context, and business relevance. This transforms long CVE lists into concrete remediation actions.
Risk-Based Vulnerability Management – At a Glance
- A high CVSS rating describes technical severity, but not the actual risk for your own organization.
- The context of the affected software and endpoints changes the priority of a vulnerability.
- Prioritization leads to concrete actions such as updates, installations, and deinstallations.
- The Proactive Hub combines vulnerability information with the state of your own IT environment.
A dashboard does not protect. Action does. This is how the previous article on Auto
Remediation began. But before an IT department can act, it must decide where to start.
In vulnerability management, this is often more complex than expected. Scanners and security databases continually provide new indications of vulnerabilities. Even a single
outdated application can result in numerous CVE entries. The list grows, but the available time does not.
And the pressure grows. The Mandiant M-Trends 2026 Report now estimates the median time
to exploitation of a vulnerability at minus seven days. This means: vulnerabilities are regularly exploited before a patch is even available.
Why classic vulnerability risk management reaches its limits
Most vulnerability management systems follow a simple principle: critical vulnerabilities are listed at the top, followed by high, medium, and low ratings. This creates an initial order, but it is not triage sufficient for daily operations.
Because a vulnerability with a high CVSS score (Common Vulnerability Scoring System) might affect an application installed only on three isolated test devices. Meanwhile, another vulnerability is technically rated lower but resides in a browser on nearly all endpoints. There might even be a known exploit for it, or the affected devices are used by employees with extensive privileges.
For a reliable priority, IT therefore needs additional information:
- Which software versions are actually installed?
- How many and which endpoints are affected?
- Are there indications of current exploitation?
- Which devices or user groups are particularly exposed?
- How complex and risky would remediation be?
Depending on the answers, the order in which they must be eliminated can change significantly.
From individual CVEs to security vulnerability remediation
CVE entries describe individual known vulnerabilities. However, admins rarely work at this level. They distribute a software update, change a configuration, or install/deinstall an application.
An old software version can contain ten or twenty CVEs. In a classic list, this results in ten or twenty findings. For remediation, however, a single update may suffice.
Therefore, it makes sense to shift focus from the individual CVE to the affected application and the possible action. Multiple findings can thus be consolidated into one concrete work order.
This does not artificially reduce the number of entries. Their significance becomes clearer. An admin recognizes which application causes the risk, where it occurs, and how many vulnerabilities can be eliminated with one action
What is risk-based vulnerability management (RBVM)
Risk-Based Vulnerability Management (RBVM) goes beyond evaluating vulnerabilities solely by their technical severity. Instead of viewing each vulnerability in isolation, threat landscape, affected systems, and business context are jointly incorporated into prioritization.
A sensible approach is to first compare the detected applications and versions with the actually affected version levels of a CVE. Subsequently, the relevant vulnerabilities are enriched with current threat intelligence.
This includes
- technical severity,
- known exploits,
- a forecast of how likely future exploitation is,
- and the context of the respective IT environment (e.g., test or business-critical system).
This results in a more accurate assessment than the CVSS score alone.
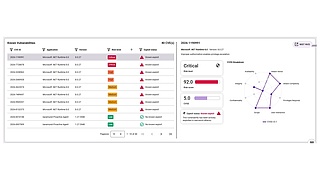
This approach becomes even more meaningful when the assessment is then linked with data from the affected endpoints. The admin then sees which application and version is affected, on which devices it occurs, and how great the need for action is in their own environment.
Prioritizing vulnerabilities – and then? How security insight becomes stable IT
Clear priority is the first step. But only the right action makes the difference. In our Best Practice Guide “DEX & UEM – Practical IT Knowledge from IT for IT,” we show how vulnerable software states become secure and higher-performing endpoints.
Not every risk requires the same remediation
Even high priority does not yet answer how a vulnerability should be remediated.
A browser or PDF reader can usually be updated quickly and broadly. For business-critical software, however, interfaces, extensions, or other dependencies may be affected. An immediate rollout to all endpoints could cause new disruptions and “digital friction” here.
For standard software, a largely automated update may be suitable. Critical applications are updated first on selected devices. Only if no new anomalies occur does another endpoint group follow.
This keeps even an urgent security measure controllable. The technical assessment shows how quickly IT should react. The endpoint and application context helps in choosing the approach.
“Why shouldn’t vulnerabilities be viewed only from a security perspective?”
Robert Klinger (Product Manager): “Because this often manifests in the same application. Outdated software runs on many endpoints, is rarely used, but causes CPU load and brings known vulnerabilities. Someone looking only at security would simply update everywhere. With endpoint context, the action becomes more targeted: active devices receive the secure version, unused installations are removed. Security and Digital Employee Experience view the same application here from different angles. The baramundi Proactive Hub brings this information together in one place.”
Conclusion: From priority to security vulnerability remediation
Thus, a long list of open CVEs does not yet indicate where an IT team should begin. Only when vulnerabilities are linked with the actual state of your own IT environment does a general security finding become a concrete, meaningful action.
After each remediation, verification follows: Was the vulnerable version actually replaced, are devices still affected, did the update cause new issues?
The baramundi Proactive Hub supports IT teams precisely in this: vulnerabilities are matched with existing endpoints, evaluated by relevance, and consolidated into concrete remediation actions.